Every security tool has a dirty secret: nobody tests whether the detector detects. The tests pass, the CI is green, and everyone moves on. Today I pointed my own scanner, mcpscan, at a set of synthetic attack files I wrote to trick it. The result: 6 of 7 fixtures fired. The one that missed taught me more than the six that passed. Here is the setup. I wrote a small harness that generates attack fi…
While it’s not unusual for everything on the dark dungeons of the IPv4 Internet to be subject to a barrage of drive-by scanner traffic and the occasional bizarrely persistent attacker, I noticed something strange while looking through my nginx logs. Persistent attack traffic coming from three particular IPs, with the strange thing being that they were arriving with Host or Referer headers from po…
TASK 2 Nmap flags a Windows 7 host with SMB on port 445, hinting at MS17-010. Which Metasploit auxiliary module would you run before loading the exploit? Answer: auxiliary/scanner/smb/smb_ms17_010 While checking the HTTP response headers during a web application penetration test, you noticed that the application does not implement the HTTP Strict-Transport-Security (HSTS) header. Which of the fol…
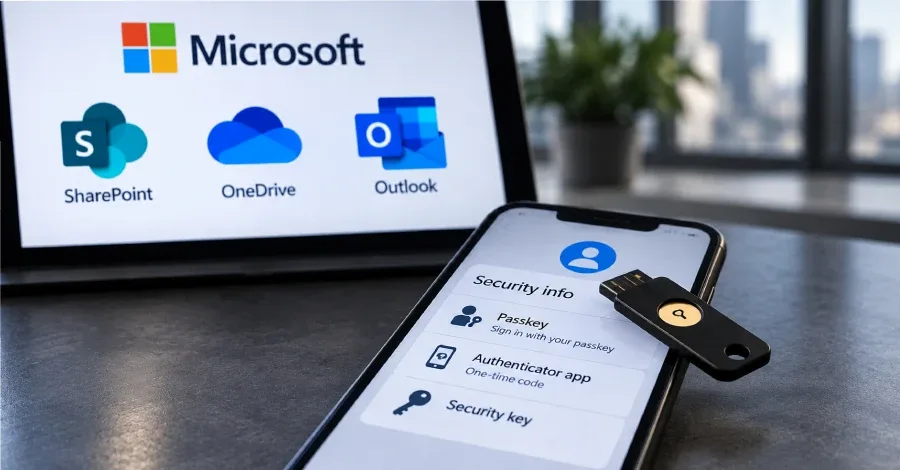
Microsoft has disclosed details of two campaigns in which threat actors are abusing third-party email delivery infrastructure to blast financial fraud scam messages and using passkey-themed social engineering to breach cloud environments.
The first campaign, per the tech giant, involved sending over a million scam emails between August 3 and 5, 2026, by masquerading as chief executive officers
Here’s an overview of some of last week’s most interesting news, articles, interviews and videos: Zero trust AI agents demand a different kind of security In this interview, Chris Webber, VP, Product Marketing at Teleport, explains why zero trust principles need to change for AI agents. He covers how agents act fast, unpredictably, and continuously, and why old ideas like least privilege and poin…
WordPress powers millions of websites around the world. One reason it is so popular is its large collection of plugins. These small pieces of software can add calendars, contact forms, online shops, security features and many other functions to a website. However, plugins may also create security risks. They add new code to a website, […] The post New Tool Uncovers Hidden Security Flaws in WordPr…
SSH manager with terminal, SFTP, AI, and SSH key store, all built in.
No plugins, no config files. One tool that handles terminals, keys, SFTP, and AI. The whole job.
Your credentials never leave your device unencrypted.
SSH tools handle real credentials for real infrastructure. Here is exactly how we protect yours.
Simple pricing.
Your cross-platform SSH manager. Start free, scale when ready.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five security flaws impacting JFrog Artifactory, ConnectWise ScreenConnect, and MikroTik RouterOS to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation in the wild.
Details of the vulnerabilities are as follows -
CVE-2026-42016 (CVSS score: 8.1) - An incorrect authorization
Big thanks to @ThreatLocker for sponsoring my trip to Black Hat USA 2026 and also for sponsoring this video. To start your free trial with ThreatLocker please use the following link: https://www.threatlocker.com/davidbombal
You can write secure C code, follow accepted best practices and still end up with a vulnerable binary. The reason is simple: the CPU does not run your source code. It runs wha…
Every Signal chat starts the same way: the client asks the Signal server for the public key associated with your contact’s phone number. But how do you know the server gave you the right key? A compromised server could provide a false public key, allowing the client to encrypt messages to an attacker rather than the intended recipient.
Until now, the only way to detect such malfeasance was to ver…
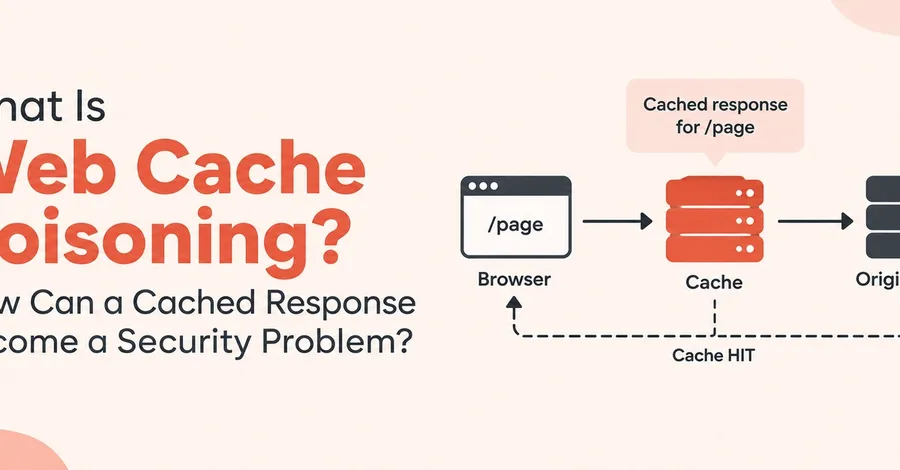
Here's something that should be completely unremarkable. A user requests /homepage . The origin server generates a response. A cache stores it. The next user requests /homepage . The cache returns the stored response without touching the origin. That's caching working as intended. It reduces latency, saves origin load, and serves popular content efficiently. Nothing suspicious. Now ask a more pre…
Cybersecurity resilience is increasingly dependent not only on technology but also on employee awareness and behaviour. Building a strong security culture can help organisations reduce cyber risks and improve their ability to respond to threats. As cyberattacks become more sophisticated, Read More ... The post Security Awareness Builds Resilience first appeared on Risk Management Association of I…

 research.io