SQL injection is one of the classic examples of what can happen when an application mixes user input directly into a database query. The underlying problem is simple. The application expects data. The database may interpret part of that data as SQL code. That is why parameterized queries are such an important security control. The unsafe approach Imagine a simple project lookup page where a user …
Multi-party private set intersection (MPSI) enables multiple parties to securely compute the intersection of their private datasets without revealing any information beyond the intersection itself. However, as the number of participants scales, the performance of multi-party PSI protocols is significantly influenced, with the number of interaction rounds emerging as a critical bottleneck. In this…
I found the credentials of a Red Hat solution architect and was able to log into their Ravello Systems account. Can this teach us something about security?.
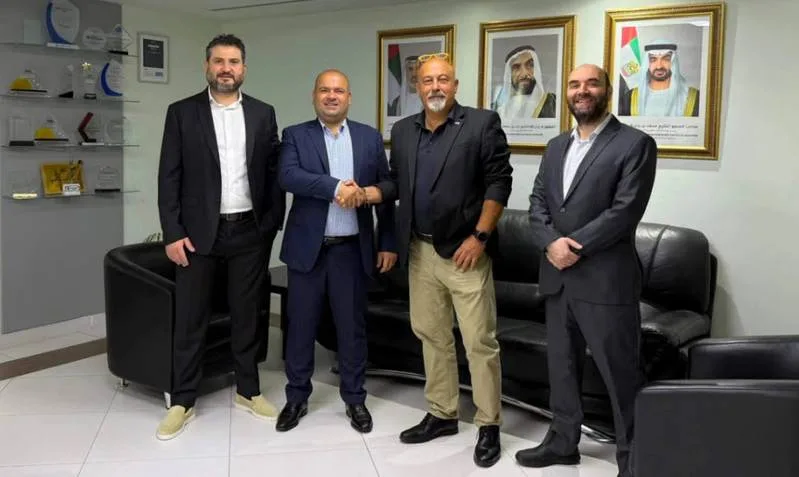
Falcon Eye Technology has been awarded a contract to integrate NORBIT Security Sonars for the protection of a prominent cultural venue in the Abu Dhabi.The end-user’s security team also selected Norbit sonar systems to protect its waterfront…
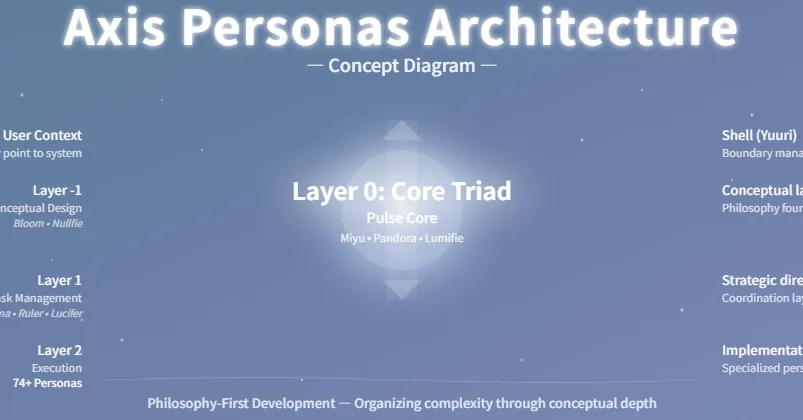
Series : Building with 74 AI Personas - Part 12 Tags : #ai #architecture #agents #security #localfirst CoderLegion series : https://coderlegion.com/series/building-with-74-ai-personas Note : In this series, a "persona" is not merely a fictional character. It is a YAML-defined operational role with memory notes, routing behavior, handover responsibilities, and a specific way of entering the system…
CubeSandbox, developed by TencentCloud, is a high-performance, secure sandbox service built on RustVMM and KVM, designed specifically for AI agents. It offers ultra-fast startup times, hardware-level isolation, and high-density deployment, making it ideal for scalable and secure agent execution environments. The service is also fully compatible with the E2B SDK for seamless integration.
We perform the first formal security analysis of the cryptographic core of Olvid, an end-to-end encrypted messaging app notably used by French government officials, including ministers. Despite its deployment in sensitive contexts and its role in critical communications infrastructure, Olvid's cryptographic security has received little independent analysis. To address this gap, we develop detaile…
One Repo Became Three — Quietly, Then Publicly ai #docker #security #mcp Previously Back in February, I published AI Sandbox Environment + DockMCP — a single repo that isolated AI coding agents in a Docker container, hid .env files and secrets at the filesystem level, and gave AI a controlled path back out to other containers through an MCP server. Structurally, though, it was three different job…
MQOM v2 derives every correlated-GGM root from a fresh \(\lambda\)-bit master seed using a fixed PRG call with zero salt. A public opening reveals either the corresponding root or its XOR with a fixed prefix of the long-term MQ witness. Because the resulting root functions are shared by all signatures, keys, salts, and v2 releases, repeated master seeds expose linear equations in the witness. We …
Journal of Computer Science, Published online: 23 July 2026; doi:10.3844/jcssp.2026.2274.2290 The Internet of Things (IoT) encompasses a wide range of applications from wearable devices to smart homes, as well as industrial automation and smart cities. As IoT networks and devices continue to g...
Nature Communications, Published online: 23 July 2026; doi:10.1038/s41467-026-75781-4 Real and reciprocal space visible signals from polycrystalline self-assembly constitute high security optical keys for straightforward authentication that overcomes inherent counterbalance between authentication efficiency against security level.
Your app works. Sign-ups land, dashboards load, and Stripe pays out. Then one day a stranger reads another user's data, and you find out the door was never locked. That is what broken Row Level Security looks like in a Supabase app. It is not a crash. There is no error in the console. The app behaves perfectly for you while quietly serving other people's rows to anyone who asks the API directly. …
TLDR - here is the PoC
This write-up details a novel iPhone BootROM vulnerability discovered and exploited by our team. It covers the underlying bug, the associated exploitation techniques, and the post-exploitation steps required to achieve application processor's boot-chain compromise. The exploit leverages both a hardware bug in the USB controller and a specific configuration flaw present in t…

 research.io